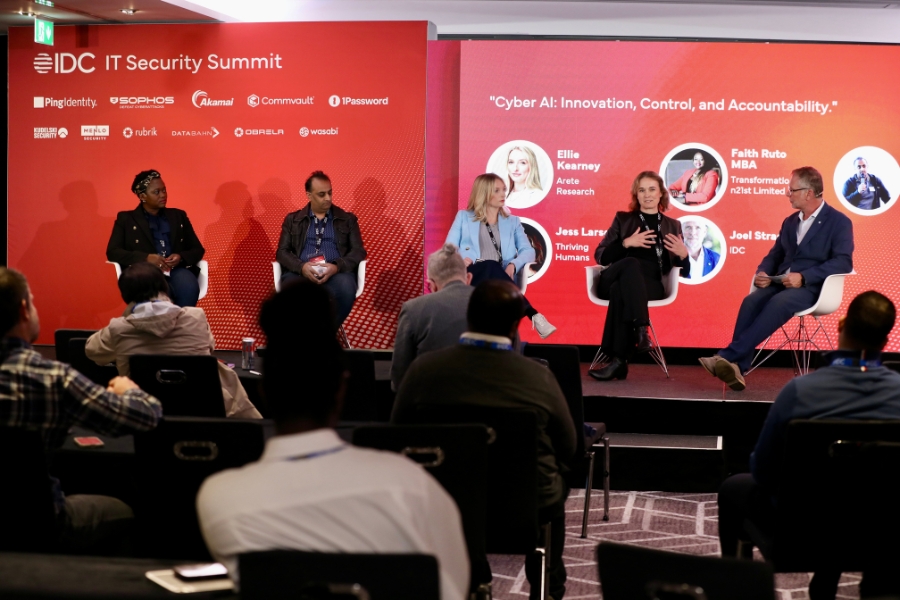
IT Security Summit Milano
Fiducia, resilienza e controllo nell’impresa autonoma
L’IT Security Summit Italia 2027 riunisce CISO, autorità di regolamentazione e leader della cybersecurity di tutto il paese per esplorare difesa basata sull’AI, cyber resilienza, sicurezza OT, AI sovrana e prontezza post-quantistica.
Con la NIS2 che ridefinisce gli obblighi per oltre 100.000 entità italiane e con le crescenti tensioni geopolitiche che aggravano il quadro delle minacce, i consigli di amministrazione italiani sono sempre più sotto pressione per trattare la cybersecurity come una priorità strategica di governance. Secondo la ricerca IDC, gli investimenti in AI sono diventati la prima priorità IT in Italia, appena davanti alla cybersecurity, mentre le due agende convergono nella pratica.
Secondo IDC, la spesa europea in sicurezza dovrebbe crescere fino a quasi 97 miliardi di dollari entro il 2028. Tuttavia, più del 40% delle organizzazioni europee ha subito una riduzione del budget per la sicurezza nel 2025, mentre gli attacchi informatici sono aumentati del 22% su base annua, il tasso più alto a livello globale. Questa tensione tra rischio crescente e investimenti limitati definisce la sfida dei responsabili della sicurezza in Europa nel 2027.
Il summit offre approfondimenti strategici e occasioni di confronto tra pari alle imprese italiane alle prese con NIS2, DORA, AI Act dell’UE e il contesto di minacce più complesso della storia digitale del paese.
Perchè Partecipare:
Dalla strategia all’azione: le priorità della cybersecurity
Acquisisci una visione strategica delle sfide di sicurezza che stanno trasformando le imprese europee: dalle minacce potenziate dall’intelligenza artificiale e dai requisiti di sovranità digitale alla resilienza OT e alla preparazione all’era quantistica. Porta con te framework operativi, insight dal confronto con altri professionisti e una roadmap concreta per affrontare uno degli scenari di cybersecurity più esigenti d’Europa.
- Governare gli agenti AI nel rispetto dei requisiti di conformità di NIS2, DORA e AI Act dell’UE.
- Rilevare e contrastare le minacce potenziate dall’AI, le identità sintetiche e i deepfake.
- Rafforzare la sicurezza OT e la resilienza delle infrastrutture critiche nelle operazioni europee.
- Prepararsi alla crittografia post-quantistica e alle roadmap di migrazione quantistica dell’UE e del Regno Unito.
- Gestire le identità di persone, macchine, API e agenti AI negli ambienti ibridi.
- Allineare gli investimenti in cybersecurity all’esposizione normativa, alle responsabilità del board e alla resilienza del business.
Roberta Bigliani
Roberta Bigliani is a Group Vice President at IDC, and Global Lead for Energy Insights, Retail Insights, and the IDC Industry Hub.
She leads IDC’s global research, data, and custom delivery agendas for energy, utilities, and retail, and oversees the Industry Hub, which drives cross-industry initiatives and collaboration.
A recognized expert in industry and business transformation, with longstanding experience in energy and utilities, Roberta’s work centers on how AI and digital technologies are reshaping the industry – enabling new business and operating models, enhancing operations and customer experiences, and effectively integrating IT and operational technology.
Her work combines deep sector expertise with a cross-industry lens, helping organizations understand how disruption and innovation propagate across sectors and markets.
Roberta regularly advises senior managers and executives at both technology suppliers and end-user organizations, speaks at international conferences, and moderates executive-level discussions.
She is based in Milan, Italy.
Massimiliano Claps
Massimiliano (Max) Claps is the research director for the Worldwide National Government Platforms and Technologies research in IDC’s Government Insights practice. In this role, Max provides research and advisory services to technology suppliers and national civilian government senior leaders in the US and globally. Specific areas of research include improving government digital experiences, data and data sharing, AI and automation, cloud-enabled system modernization, the future of government work, and data protection and digital sovereignty to drive social, economic, and environmental outcomes for agencies and the public.
BACKGROUND
Max Claps has over 20 years of public sector experience. After starting his career as a management consultant, he joined IDC in 2002 as the lead analyst for the government, healthcare, and education industries in Europe. He has since held various analyst and management roles at IDC working as an advisor to technology suppliers, public sector senior leaders and policymakers throughout North America, Europe, the Gulf Region, Asia-Pacific, and Latin America. He focused on helping public sector organizations realize the benefits of artificial intelligence, edge computing, cloud computing, shared services, digital services, smart cities, and sustainable mobility and transportation. Max also worked at Gartner, where he was research director and agenda manager for the global government research analyst team. IMax spent two years at SAP, where he was the global solution lead for the SAP Future Cities, Citizen Experience and Postal Services programs.
EDUCATION/INDUSTRY ACCOMPLISHMENTS
Claps holds a degree in international business from Bocconi University in Italy.
Throughout his career at IDC, Max Claps has been a co-author of several studies published on behalf of the European Commission on topics like eGovernment, location data and intelligence, cloud computing, and data spaces.
Max Claps has actively contributed to ITU working groups, such as the United for Smart Sustainable Cities (U4SSC) global UN initiative coordinated by ITU, UNECE and UN-Habitat, and the ITU focus group on Metaverse.
Martina Longo
Martina Longo is a research manager in the IDC EMEA Digital Business and AI Transformation Strategy Research Group. In her role she advises ICT players on how organizations create business value using digital technologies. She also leads the IDC EMEA Digital Native Business research, focused on a mix of start-ups, scaleups, and more mature digital natives. She also collaborates with the EMEA C-Suite Tech Agenda research, analyzing technology investments and buyer preferences across C-suites in the EMEA region. She also examines how C-suite leaders are evolving as a result of key market trends and technology innovations (e.g., AI).
Andrea Siviero
Andrea Siviero leads IDC’s European Digital Business and Future of Work Research group. The group provides market research insights to foster a purposeful and fair adoption of technologies supporting digital societies, businesses and workforce and empower tech providers in strategic decision making, planning and go-to-market activities. Siviero also co-leads the IDC Worldwide MacroTech Research program, focused on the intertwined connection between the Economical and Digital worlds – analyzing the impact key MacroEconomic factors have on the digital landscape and viceversa, how technologies are impacting economies around the world.
Siviero advises IT players on building a forward-looking digital business and workforce strategy, while providing an in-depth view on future of work technology adoption, key digital use cases, macroeconomic digital impact, and digital regulations and emerging technology, via qualitative subscriptions and custom consulting projects. He has extensive experience with large strategy and go-to-market projects with IT providers. He is a member of IDC’s global Tech Storytellers taskforce and he is passionate about public speaking and customer engagement opportunities.
He joined IDC’s European team in 2014 and has become a recognized independent analyst across Europe and beyond in the vertical markets and digital business space. He is based in Italy and he holds a joint PhD in mathematics between the Université Bordeaux I (France) and the Universiteit Leiden (the Netherlands). During his PhD, he covered scientific research, academic teaching, and vocational training. He is a native Italian speaker and he is fluent in English and French.
Joel Stradling
As research director for IDC’s European Security practice, Joel Stradling leads the content and analyst team for tracking the European security segment. His main focus area is the integration of network plus security and evolution of network architectures towards software-defined secure access.
Stradling has 20 years of experience as an analyst of international managed enterprise network and IT services. He is a regular speaker at major industry conferences talking about emerging technologies in B2B enterprise network and IT and wholesale carrier-to-carrier services. Joel is a well-known and highly regarded expert in the industry, offering insight and advice to C-level executives on technology competitive landscapes and emerging technologies, such as SD-WAN, 5G, SDN/NFV, and cyber-security.
Thomas Mascioli Colavecchi
Appassionato di Security Governance con esperienza pluriennale, è stato consulente ed imprenditore nel settore fino al 2011. Nel 2012 entra in CDP, dove nell’arco di 10 anni ha posto le fondamenta della governance di sicurezza allineandola alle migliori pratiche di settore. Dal gennaio 2023 ha assunto il ruolo di Chief Information Security Officer di Polo Strategico Nazionale, che ha portato in poco più di un anno a certificarsi ISO 27001, ISO 23301 e CSA STAR LEVEL 2, ed a qualificare i servizi e l’infrastruttura PSN al massimo livello consentito dalle normative applicabili (Q*4).
Giovanni Zanetti
Stefano Righetti
Luca Della Giovanna
Tematiche principali
Proteggere l’AI in un continente regolamentato
Come le imprese europee possono governare gli agenti AI e i sistemi autonomi nel rispetto dei vincoli di NIS2, DORA e AI Act dell’UE, mantenendo fiducia operativa, responsabilità e conformità in ambienti sempre più guidati dall’AI
La corsa agli armamenti cyber in Europa
Come l’AI intensifica sia il cybercrimine sia la difesa informatica in Europa: gli avversari sfruttano identità sintetiche e deepfake, mentre i team SOC europei si affrettano a adottare rilevamento, risposta e generazione dinamica di playbook basati sull’AI
Identità e accessi nell’impresa post-perimetro
Come l’identità è diventata il livello di controllo critico per le imprese europee alle prese con il cloud ibrido, i requisiti di governance degli accessi della NIS2 e la crescita esplosiva delle identità non umane, inclusi agenti AI e accessi machine-to-machine
Proteggere la supply chain digitale europea
Gli attacchi alla supply chain sono diventati uno dei vettori di minaccia più rilevanti per la cybersecurity in Europa. Questo tema esplora come le organizzazioni europee rafforzano la software assurance, la gestione del rischio verso terze parti ai sensi della NIS2 e le pratiche di AI bill of materials, mentre il 65% delle implementazioni di AI agentica in Europa si avvia verso requisiti BOM entro il 2027.
Rischio cyber, consigli di amministrazione e obbligo di conformità in Europa
I consigli di amministrazione europei hanno responsabilità senza precedenti, poiché NIS2 e DORA attribuiscono ai dirigenti una responsabilità diretta nella gestione del rischio cyber. Questo tema esamina come i leader e i board europei quantificano il rischio, allineano gli investimenti in sicurezza all’esposizione finanziaria e operano nel contesto normativo più esigente al mondo.
Sovranità, regolamentazione e fiducia digitale
Come l’AI Act dell’UE, gli obblighi di residenza dei dati, la NIS2, la DORA e i requisiti di cloud sovrano stanno ridefinendo architettura e governance delle imprese in Europa. Con il 40% dei governi europei che entro il 2028 imporrà l’AI sovrana, la posta in gioco per la pianificazione strategica non è mai stata così alta.
2027 Prediction
25% delle imprese europee utilizzerà piattaforme di quantificazione del rischio cyber basate su agenti autonomi per trasformare le metriche di sicurezza in esposizione finanziaria, orientando budget, controlli e valutazioni del rischio nelle operazioni di M&A.
Come partecipare
L’evento, che si terrà l’11 maggio 2027 a partire dalle ore 9:00, è a partecipazione gratuita (previa compilazione del modulo di registrazione) per i professionisti appartenenti ai seguenti settori: Manufacturing, Automotive, Fashion, Finance, Banking and Insurance, Retail, Energy and Utilities, Media, Government, Health, Education, Transports, Logistics, Telecommunications, Personal and Professional Services.
L’accesso all’evento non è consentito ad aziende ICT non sponsor (vendor, distributori, reseller, VAR, system integrator), società di consulenza e servizi ICT, privati e liberi professionisti.
La lingua ufficiale dell’evento è l’italiano.
Knowledge Hub
The NIS 2 directive – where are we now?
The deadline for the transposition of the EU’s second Network and Information Systems Security directive (NIS 2) came and went in October 2024 with only a handful of member states having completed the task.
European ICT spending implications of NATO’s 5% GDP spending target
At the 2025 NATO Summit in The Hague a few weeks ago, member states pledged to allocate 5% of their annual GDP to core defense requirements and defense- and security-related expenditures by 2035.
IAM 2025: The Rise of the Machines
Identity and access management (IAM), and by extension, identity security, is one of the most pervasive and impactful challenges facing all European organizations today, from an operational and risk management perspective.
Non è l'evento giusto per te?
Non preoccuparti, abbiamo tanti altri eventi che possono fare al caso tuo! Iscriviti per ricevere i nostri inviti e ti invieremo un messaggio non appena avremo un nuovo evento che pensiamo possa interessarti.
Sign up